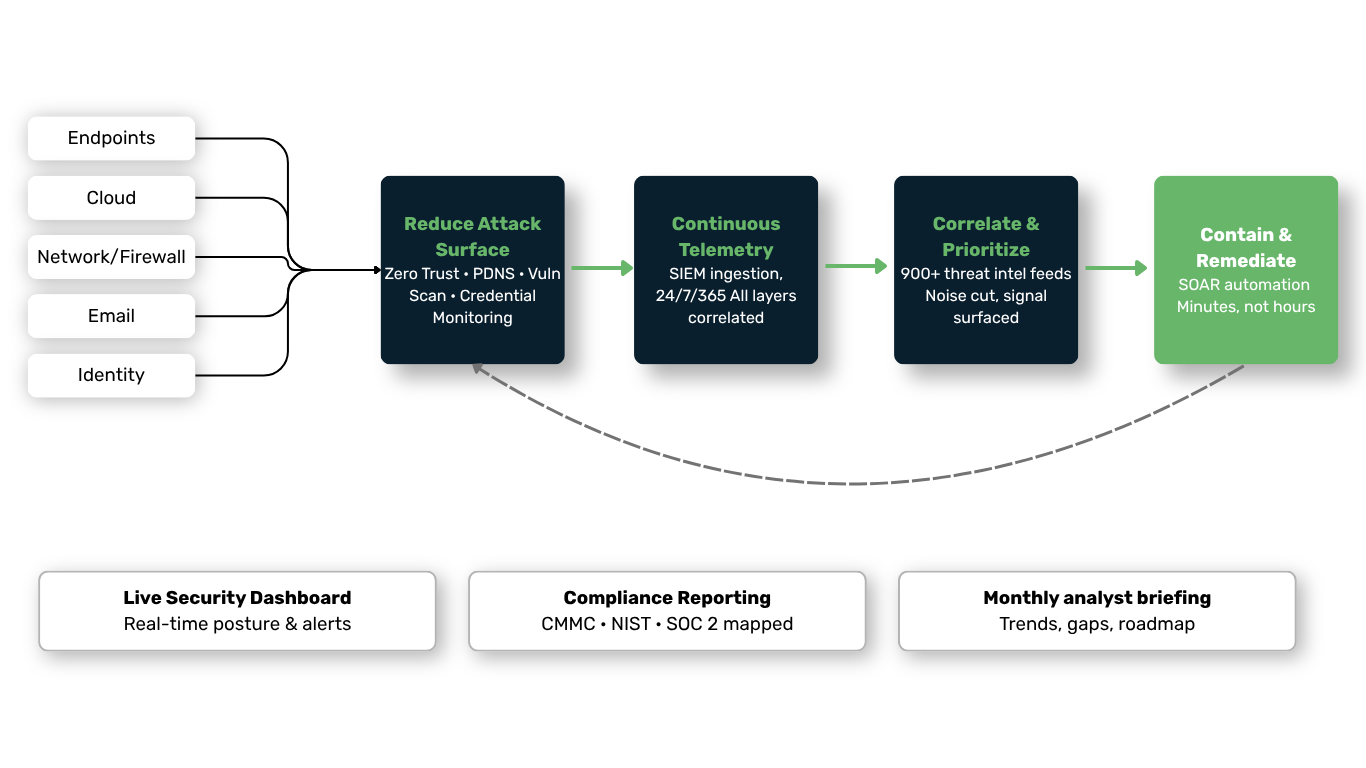
Cyberleaf's managed security platform follows a continuous lifecycle, fusing expert analysts with MDR/XDR technology to monitor, detect, and respond to threats while proactively hardening your environment against the next attack.
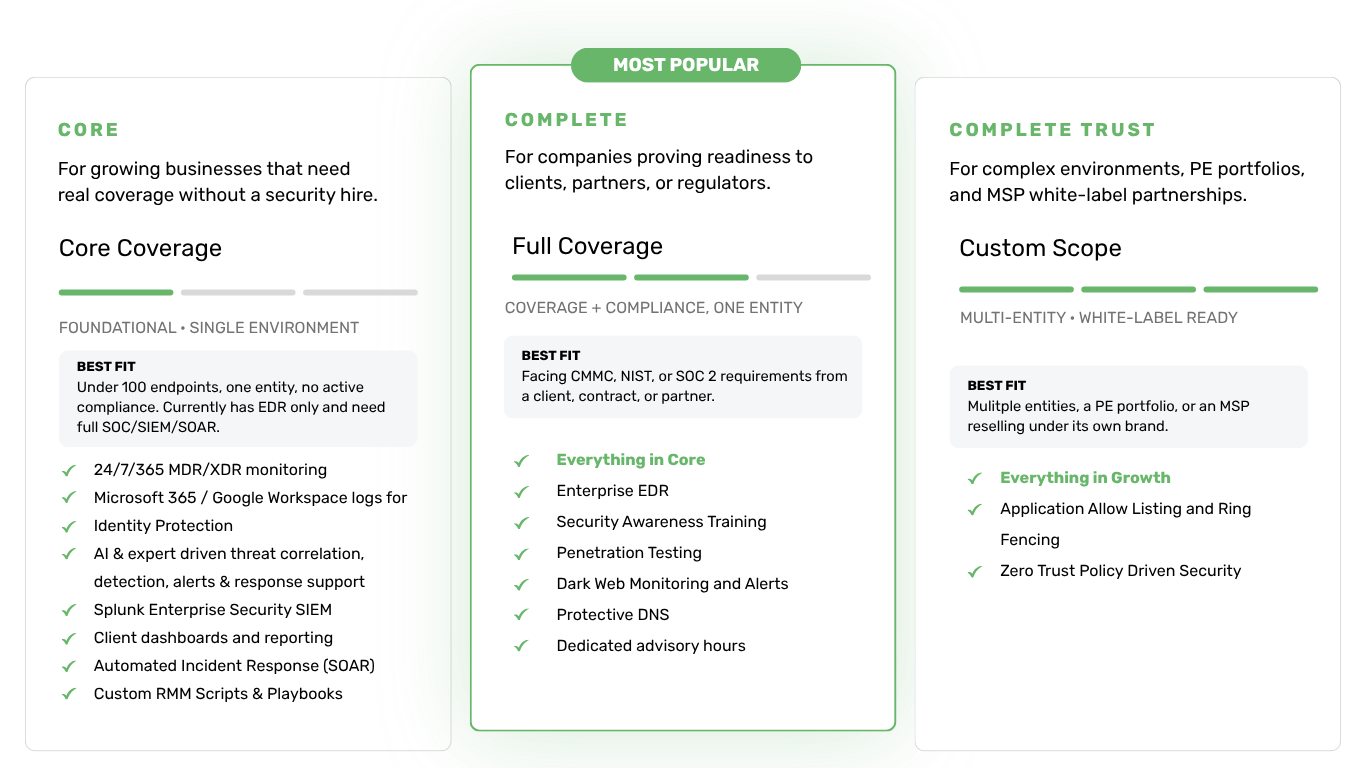
Most of our customers select one of the following three packages, we work with each one to make sure you have a plan that works for your business.
Real-time visibility across cloud infrastructure, endpoints, networks, firewalls, servers, email platforms including Microsoft 365 and Google Workspace, identity and access management, web activity, and data assets.
Cyberleaf’s managed SIEM platform leverages top-tier EDR and XDR technology to deliver security analytics at scale. By correlating telemetry from your environment with intelligence from more than 900 threat feeds, we identify and stop threats that conventional tools miss.
Cyberleaf’s SOAR (Security Orchestration, Automation, and Response) platform orchestrates and automates incident response workflows, enabling faster and more efficient threat remediation. Automated containment actions, such as host isolation and credential re-authentication, blunt the impact of attacks in minutes, not hours.
Schedule a call with one of our experts. No obligation, we'll help you talk through gaps, priorities, and next steps.
A managed security service provider (MSSP) typically focuses on monitoring logs and forwarding alerts to your internal team for investigation. MDR goes further by providing hands-on threat investigation, proactive threat hunting, and active incident response. With Cyberleaf’s MDR service, threats are not just detected, they are investigated and contained by our security analysts.
Protective DNS blocks access to known malicious domains at the DNS layer before a connection is ever established. This stops phishing, malware command-and-control callbacks, and data exfiltration attempts at the earliest possible stage, adding a critical layer of proactive defense to your environment.